Anti-Keylogger Protection
ACTIVEAdds a protective layer against keylogging and credential capture, with user-confirmed actions to reduce unwanted blocking.
Helps stop: keyloggers, credential stealers, form-grabbers
Features
A real-time IDS built to work alongside your antivirus. Where traditional antivirus relies on signatures, MZGuard watches for suspicious activity, to reduce the risk from malware, ransomware, script abuse and advanced attack patterns.
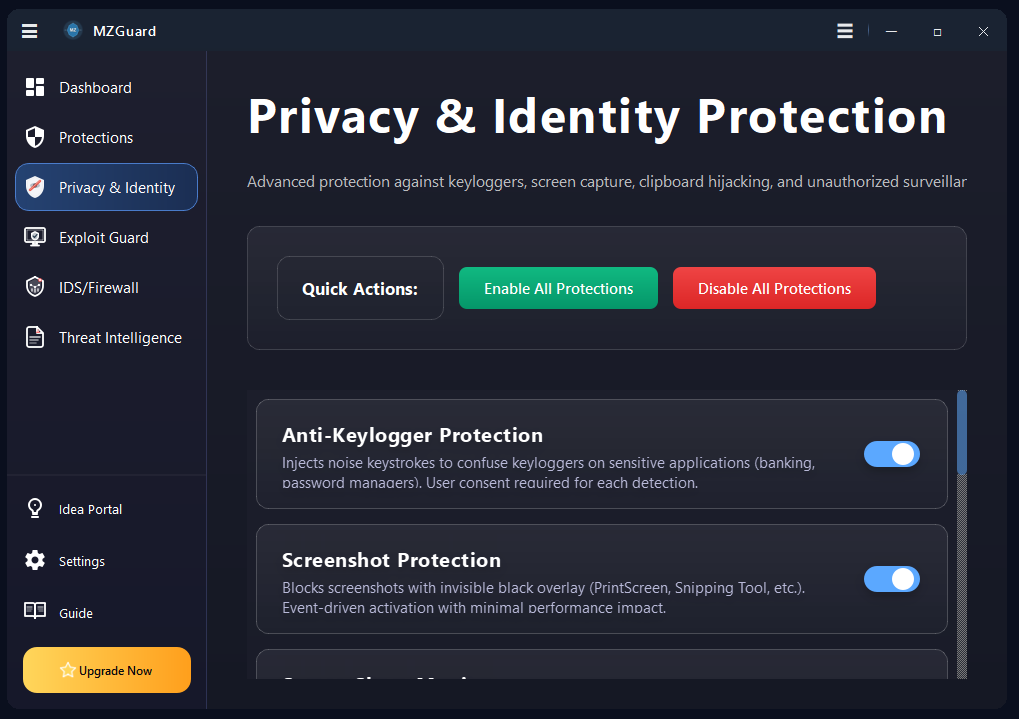
Privacy & identity
Clear, user-controlled protections. You decide when an action is allowed, and every decision is visible.
Adds a protective layer against keylogging and credential capture, with user-confirmed actions to reduce unwanted blocking.
Helps stop: keyloggers, credential stealers, form-grabbers
Blocks screenshots on sensitive workflows with an invisible protection layer, helping prevent accidental or malicious exposure.
Helps stop: screen scraping, confidential data leakage
Monitors screen sharing in browsers and conferencing apps, and asks for explicit consent before capture or broadcast.
Detects suspicious clipboard changes, such as address or IBAN swapping, and helps prevent silent payment redirection.
Helps stop: clipboard hijackers and address swapping
Monitors webcam access system-wide, with OS-level blocking and allow or deny decisions for trusted applications.
Monitors microphone access system-wide, with OS-level blocking to reduce the risk of silent recording.
Detects and blocks clipboard address substitution during crypto transfers, with real-time monitoring and actionable alerts.
Helps stop: crypto address hijacking and payment redirection
Detects and blocks IBAN or code substitution during copy and paste in bank transfers and invoice workflows.
Helps stop: banking stealers and invoice redirection
Privacy panel
Each protection shows its status and the decisions it has taken, so nothing changes silently.
Security & threat prevention
Multi-layer defense against ransomware, APT activity and emerging techniques.
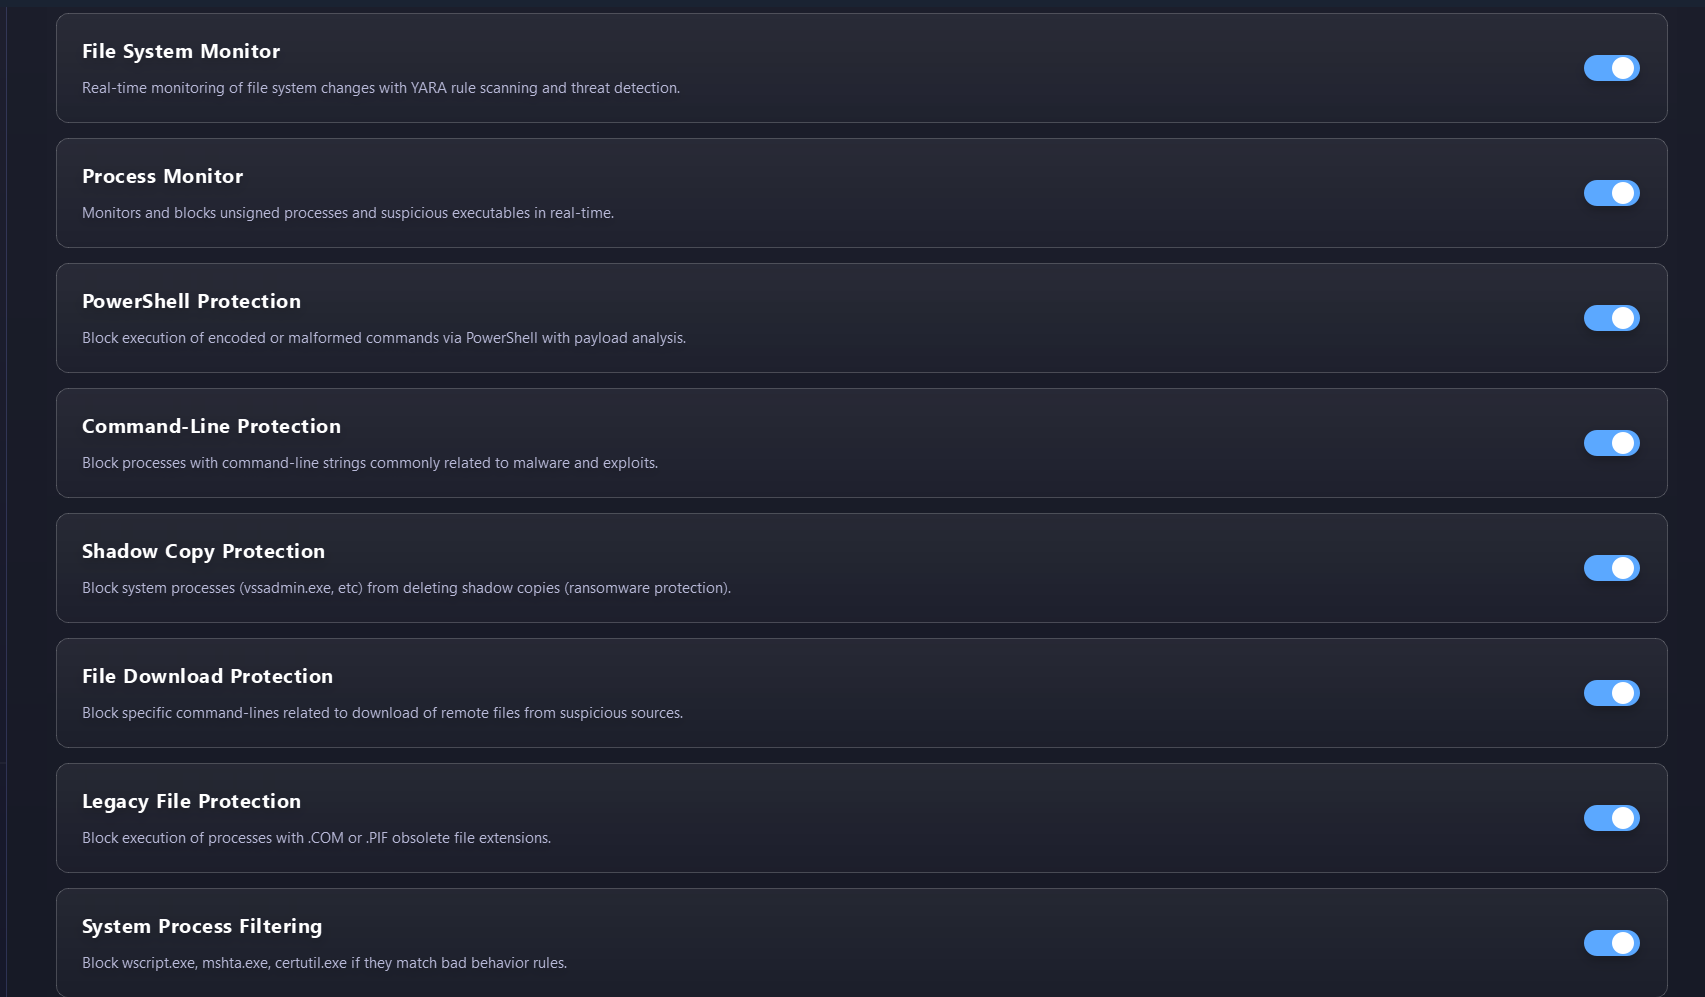
Detects ransomware-like patterns such as mass changes and rapid renames, and can interrupt them.
Watches for injection, hollowing and abnormal parent-child process chains.
Flags encoded or obfuscated scripts and blocks high-risk command flows.
Detects destructive commands and protects against backup sabotage.
Helps keep restore points available, and blocks suspicious removal attempts.
Scans downloads before they run, and offers block, quarantine or allow actions.
Adds guardrails around document and attachment workflows often used for first-stage compromise.
Checks the identity of critical Windows processes to catch lookalike malware.
Prevents boot configuration tampering used to reduce recovery options.
Monitors removable media and blocks suspicious autorun-style execution.
Detects persistence attempts such as startup entries, scheduled tasks and WMI.
System hardening
Harden Windows, detect tampering and speed up incident response with clear logs.
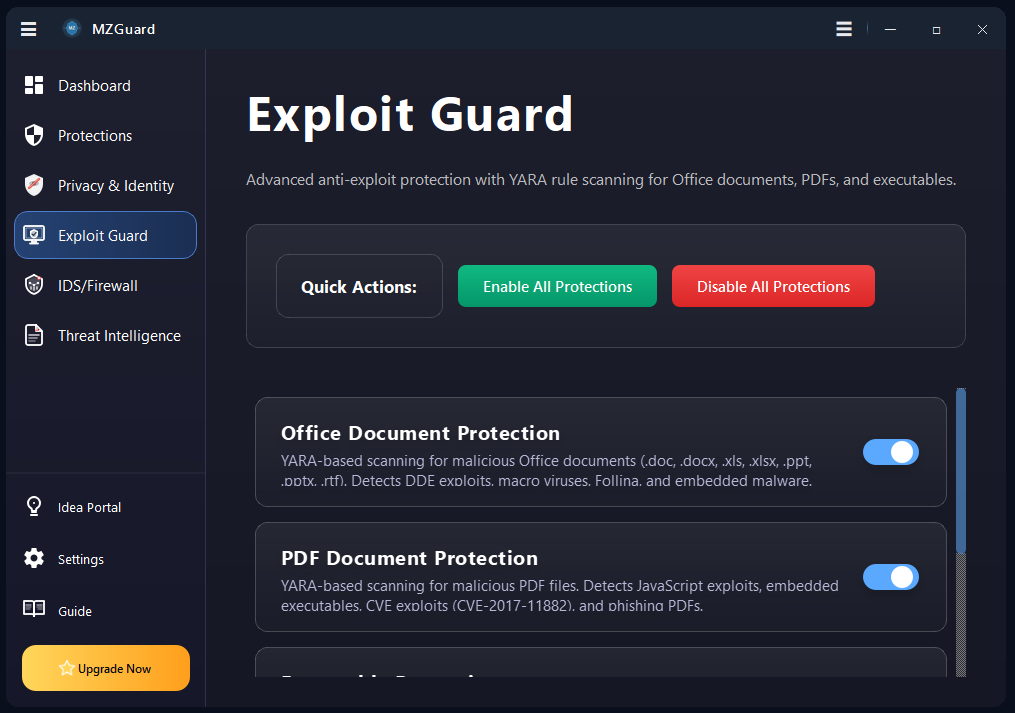
Exploit Guard
YARA-driven exploit defense that scans the high-risk carriers attackers use: documents, PDFs, executables and downloads.
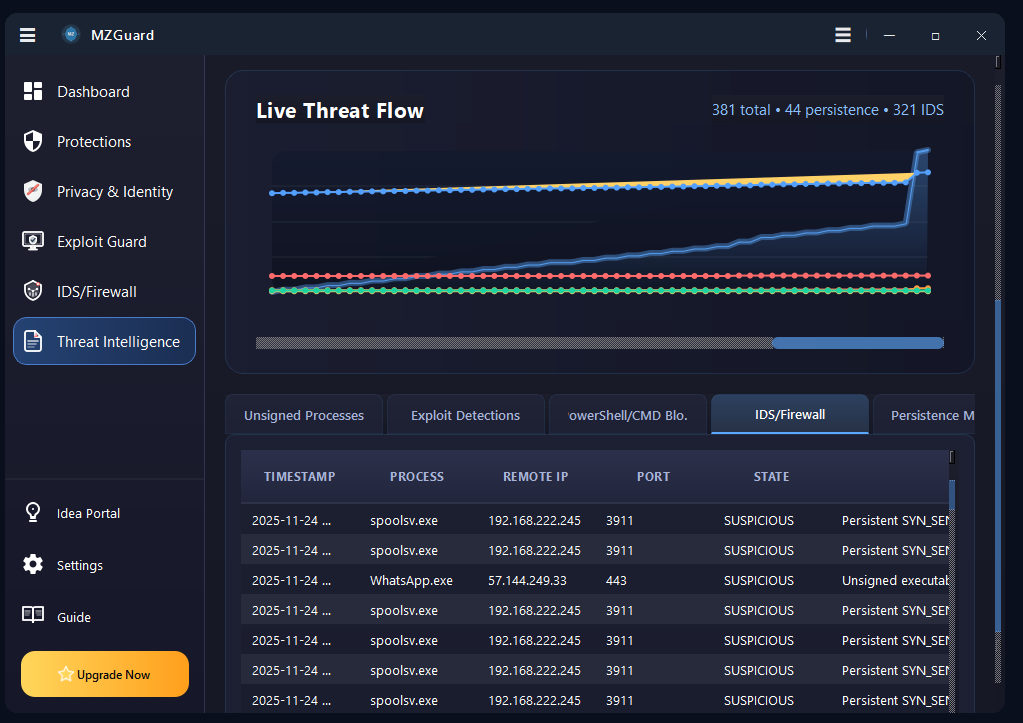
Security logs
A unified event timeline across all modules, with live visibility and context you can export for IT or your SOC.
A hardening checklist that flags weak or tampered settings, such as Defender, firewall profiles and services, with guided fixes.
Isolate suspicious files for later review, keep blocks in place for recurring detections, or allow an item with a recorded reason.
Tune protection without turning it off. Allow trusted tools, and keep high-risk behavior monitored.
Ransomware & devices
Early warning for ransomware, automatic backups and protection against keystroke injection from unknown USB devices.
Protected zones where your data matters, early warning signals, clear severity levels, and a recovery workflow with backups and restore actions.
Detects non-human input patterns from HID-style devices, and helps prevent scripted keystroke injection. Trusted devices are allowlisted.
Monitors removable media and blocks suspicious autorun-style execution, with optional rule-based checks on insertion.
Enhanced IDS / Firewall
Real-time network monitoring, curated rules and enforcement in Windows Firewall, so blocking is visible and controllable.
Download the free edition and see the suite on your own Windows machine.